
Commit Signing
CodeFloe signs the commits it creates itself with an instance SSH key. This lets you merge pull requests from the web UI into branches protected with Require signed commits.
What the instance signs
Section titled “What the instance signs”- Merge commits and squash commits created when you merge a pull request.
- Commits made in the web editor.
- The initial commit of a new repository.
These commits show as verified and are credited to the CodeFloe organization: it is both the committer and the signer, and you remain the author.
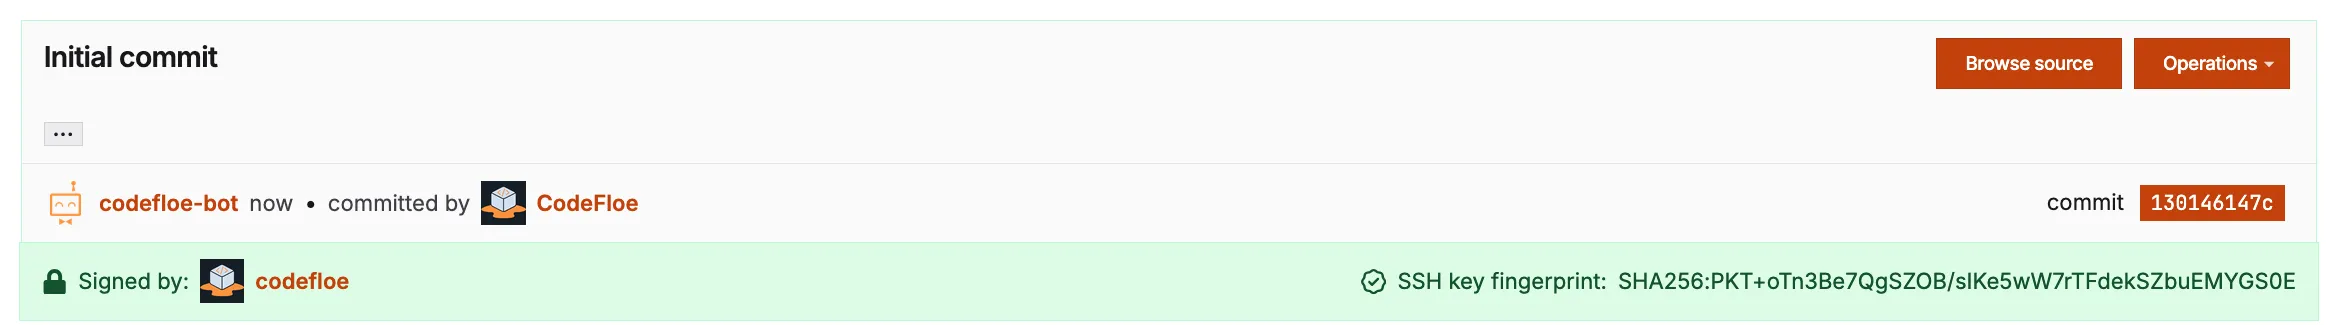
Commits you push yourself are not touched: sign them with your own SSH or GPG key as usual.
The Rebase then fast-forward and Rebase then create merge commit styles rewrite the pull request’s commits when it is behind the target branch. The rewritten commits lose your signatures and the instance does not re-sign them, so a branch that requires signed commits rejects the merge. Use Create merge commit or Create squash commit instead, or bring the pull request up to date with signed commits first.
When a merge is signed
Section titled “When a merge is signed”The instance only vouches for a merge when everything underneath is already trustworthy. It signs a pull request merge only if all of the following are true:
- The person merging has an SSH or GPG key added under Settings → SSH / GPG keys.
- The person merging has two-factor authentication enabled.
- The latest commit on the target branch is verified.
- Every commit in the pull request is verified.
Web editor commits follow the same idea: they are signed when you have a key and two-factor authentication enabled and the parent commit is verified.
If any condition is missing, the commit is not signed, and a branch that requires signed commits blocks the merge.
Verifying instance signatures locally
Section titled “Verifying instance signatures locally”The public key is served at https://codefloe.com/api/v1/signing-key.ssh.
Its fingerprint is:
| Key type | SHA256 fingerprint |
|---|---|
| ED25519 | SHA256:PKT+oTn3Be7QgSZOB/sIKe5wW7rTFdekSZbuEMYGS0E |
To check the key you download against this fingerprint:
Git verifies SSH signatures against an allowed signers file. Add the CodeFloe key to it:
Then git log --show-signature reports instance-signed commits as a good signature for codefloe@noreply.codefloe.com.
Troubleshooting
Section titled “Troubleshooting”A protected branch still blocks the merge
Section titled “A protected branch still blocks the merge”Go through the conditions in When a merge is signed:
- Add an SSH or GPG key to your account and enable two-factor authentication.
- Make sure every commit in the pull request shows as verified; rebase and re-sign any that do not.
- If you used one of the rebase styles, switch to Create merge commit or Create squash commit, see What the instance signs.
- If the branch was protected after unsigned commits had already landed, its latest commit is unverified. Push one signed commit to the branch, or merge one pull request with the Fast-forward only style. That style creates no new commit, so it works when the pull request is up to date with the branch and all its commits are signed.
If you run into an issue, please open a topic in the CodeFloe forum.